Models, tools, agents: put each control in the right place
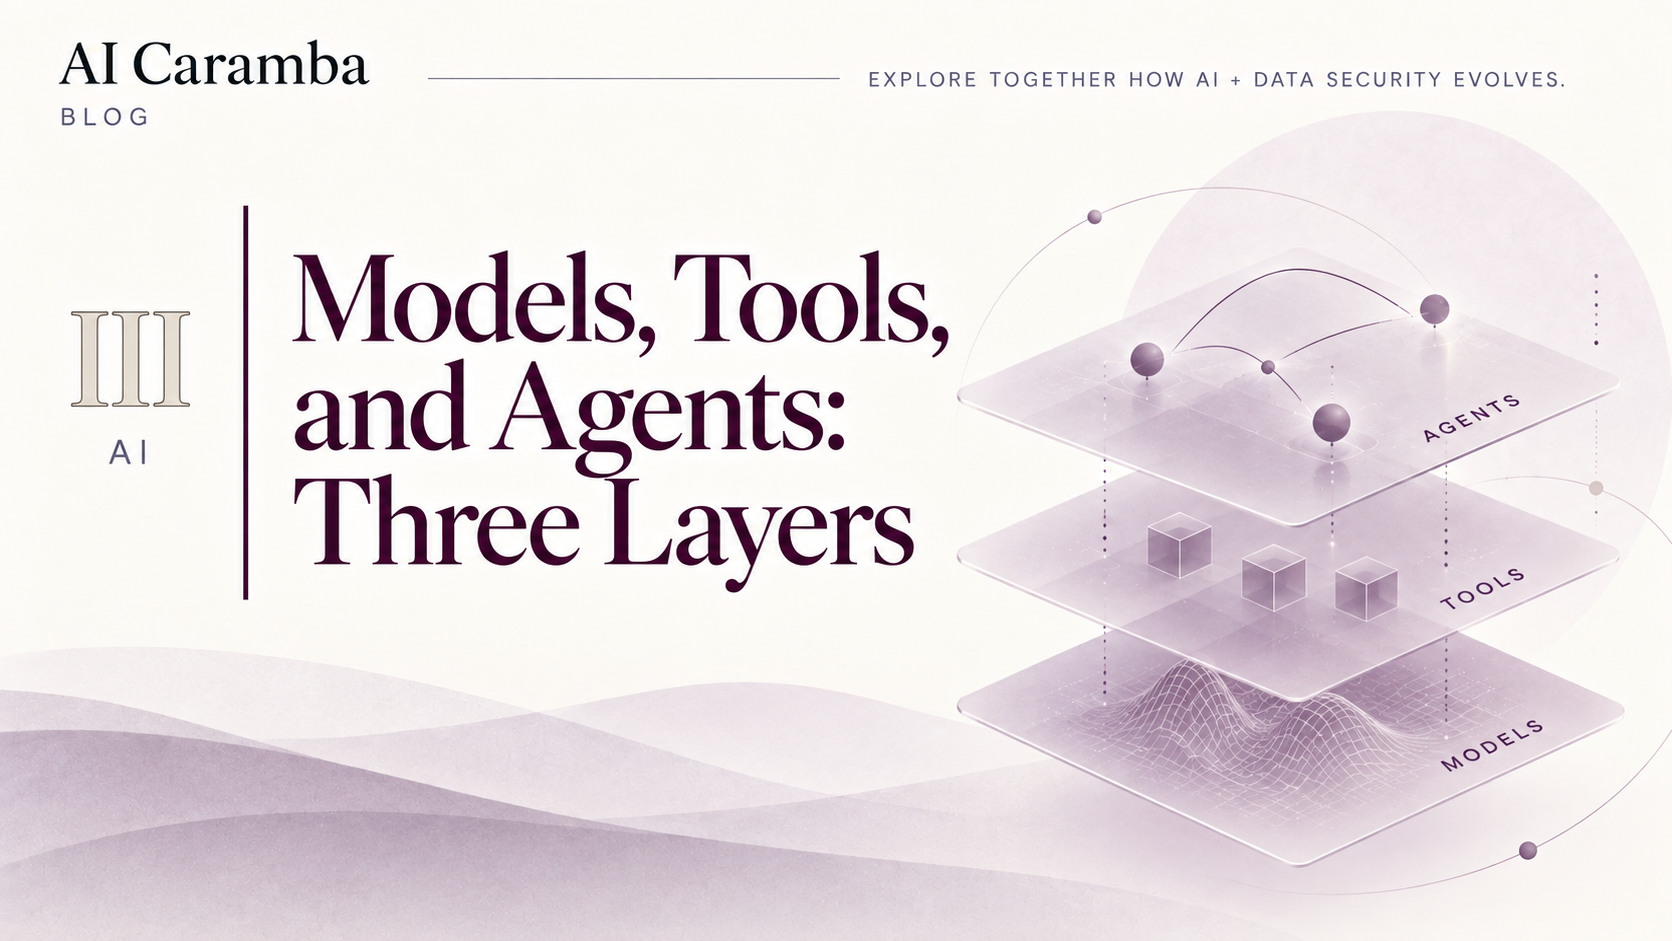
A model proposes output. A tool performs an operation. An agent loop decides what happens next. Map each safety rule to the component that enforces it.
Revised
I Identify the mechanism
A chat interface can combine a generator, a tool executor, and a loop that selects successive steps. Their responsibilities determine where controls belong.
OpenAI's function-calling documentation describes the sequence: the model emits a function call, application code executes it, and the result returns to the model. Hosted built-in tools use their own executor. Each execution path needs an authorization decision.[1]
II Three failures, three places to intervene
| Failure | Enforcement point | Useful check |
|---|---|---|
| The answer is wrong | Acceptance and output validation | Reject a result that fails the task's criteria |
| A call exceeds the user's permission | Tool or resource boundary | Deny the operation even when its arguments look valid |
| The run repeats or expands its work | Agent runtime | Stop dispatching when scope or limits are exceeded |
OWASP recommends least privilege and approval for high-risk actions as part of prompt-injection mitigation. Prompt-injection risks persist in systems using retrieval or fine-tuning.[2]
A permitted read can send confidential material into a new processing or storage boundary. Follow those copies in the article on sensitive information in AI workflows.
III Test denied actions and revoked grants
Proposed acceptance tests: use an isolated fixture, request an allowed operation, then request one outside the granted scope. Deny an approval and verify that no action occurred. Revoke a grant during a paused run and verify that the next attempted operation is refused.
Technical note · authorize each resource and operation
A schema-valid request can target the wrong tenant, document or recipient. Derive the acting identity from the authenticated session. Validate that identity's access to the specific resource and operation at execution time.
Stopping a loop prevents new dispatches. In-flight external requests may require explicit cancellation, and completed effects may require reconciliation or compensation. Audit attempted, authorized and completed operations separately.
Before enabling a connector, define what it may read, what it may change, and what will stop it. Verify each boundary through the component that enforces it.
Sources & review
Sources checked 2026-09-21. Control designs and test protocols are editorial recommendations.